Network Operations Center
From SD-WAN to Wi-Fi, we track uptime, latency, and loss in real time and act before users feel it. Post-incident reviews add up to long-term reliability.
24×7×365 Network & Security Operations Center24×7 NOC & SOC
Managed Security
Steady monitoring with clear updates, so you always know what’s happening. Our 24×7 Security and Network Operations Centers turn alerts into fast, evidence-backed action.
Coverage
Our SOC hunts, verifies, and contains threats by isolating accounts or hosts, blocking malicious traffic, and coordinating clean recoveries with minimal disruption.
From SD-WAN to Wi-Fi, we track uptime, latency, and loss in real time and act before users feel it. Post-incident reviews add up to long-term reliability.
Our SOC watches continuously, verifies true positives fast, and executes playbooks to contain threats before they spread, with plain-English updates and evidence.
We detect real threats fast, verify the signal, and contain them by isolating affected users or systems before the impact spreads. You get clear next steps, not just alerts.
Frontline fixes fast, with clear escalation to senior engineers. Most issues close at Tier 1–2; Tier 3 handles the hard stuff without the handoffs.
A focused walkthrough of uptime, incidents, patch and vulnerability posture, and open risks, ending with clear priorities and owners for the next 30 days.
Under attack right now?
Measured results
Sensors and rules catch suspicious activity quickly, so investigation starts while the window for damage is small.
User-reported messages are investigated quickly and pulled from inboxes to limit spread.
We don’t just wait for alarms. Targeted hunts surface quiet threats and dormant risks.
Staged rollouts balance speed and stability, closing vendor-flagged risks promptly.
Incident lifecycle
Every incident follows the same playbook, with plain-English updates at every stage and a concise after-action report at the end.
Always-on sensors and targeted hunts surface suspicious activity in minutes.
Analysts separate noise from real risk and confirm true positives fast.
Pre-approved playbooks isolate hosts, disable accounts, and block traffic.
We coordinate clean recoveries with minimal disruption to your business.
Root cause, impact, and next steps, written so leadership understands.
Managed Security team
At Armory5, we like to put a name to a face. We want you to know who’s watching your network, and that we’re always here to help.
Contact the team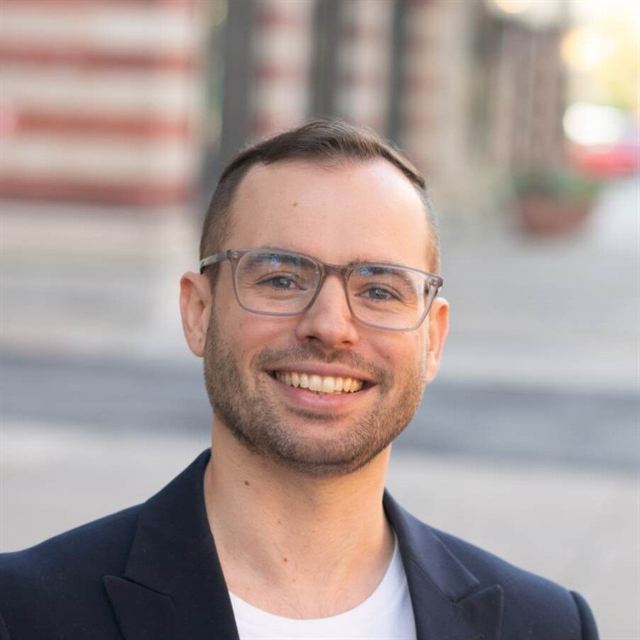
SOC Supervisor
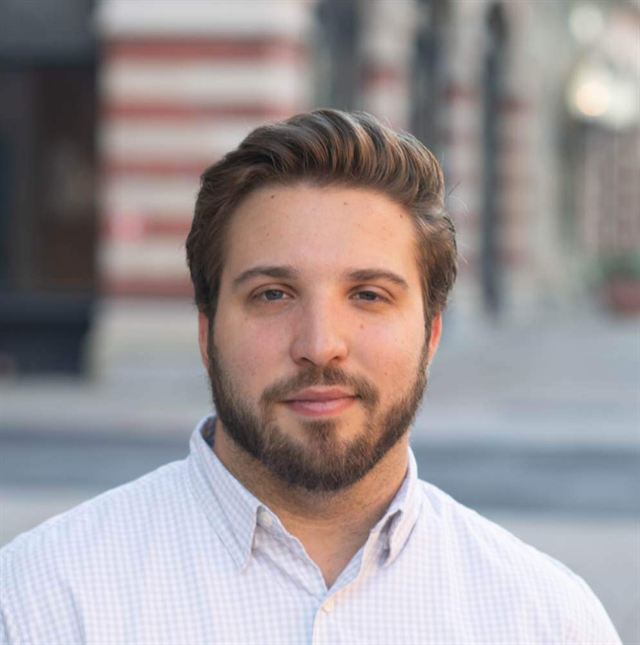
NOC Supervisor
P1 alerts get human triage within minutes, and containment begins as soon as a threat is verified. We share initial findings quickly, then follow with a concise report.
A single channel for live updates (email, phone, or Teams), an initial summary once things are stable, and a full report within the agreed SLA.
We act under pre-approved playbooks: isolating hosts, disabling accounts, and blocking traffic. Anything outside those guardrails is confirmed with you first.
Typically per endpoint or per user, with tiers for coverage and integrations. Projects and advanced forensics are scoped separately.
Free assessment
Contact us for a free assessment. We’ll put together a structured plan to secure and future-proof your business.